WHITE PAPER
Data Privacy
From GDPR to the EU AI Act
Turn your privacy program into a foundation for AI governance
Your GDPR program is a valuable starting point for AI governance.
The EU AI Act introduces distinct responsibilities. For privacy and compliance leaders, the strategic task is to determine how far existing capabilities can support them and where additional controls are needed.
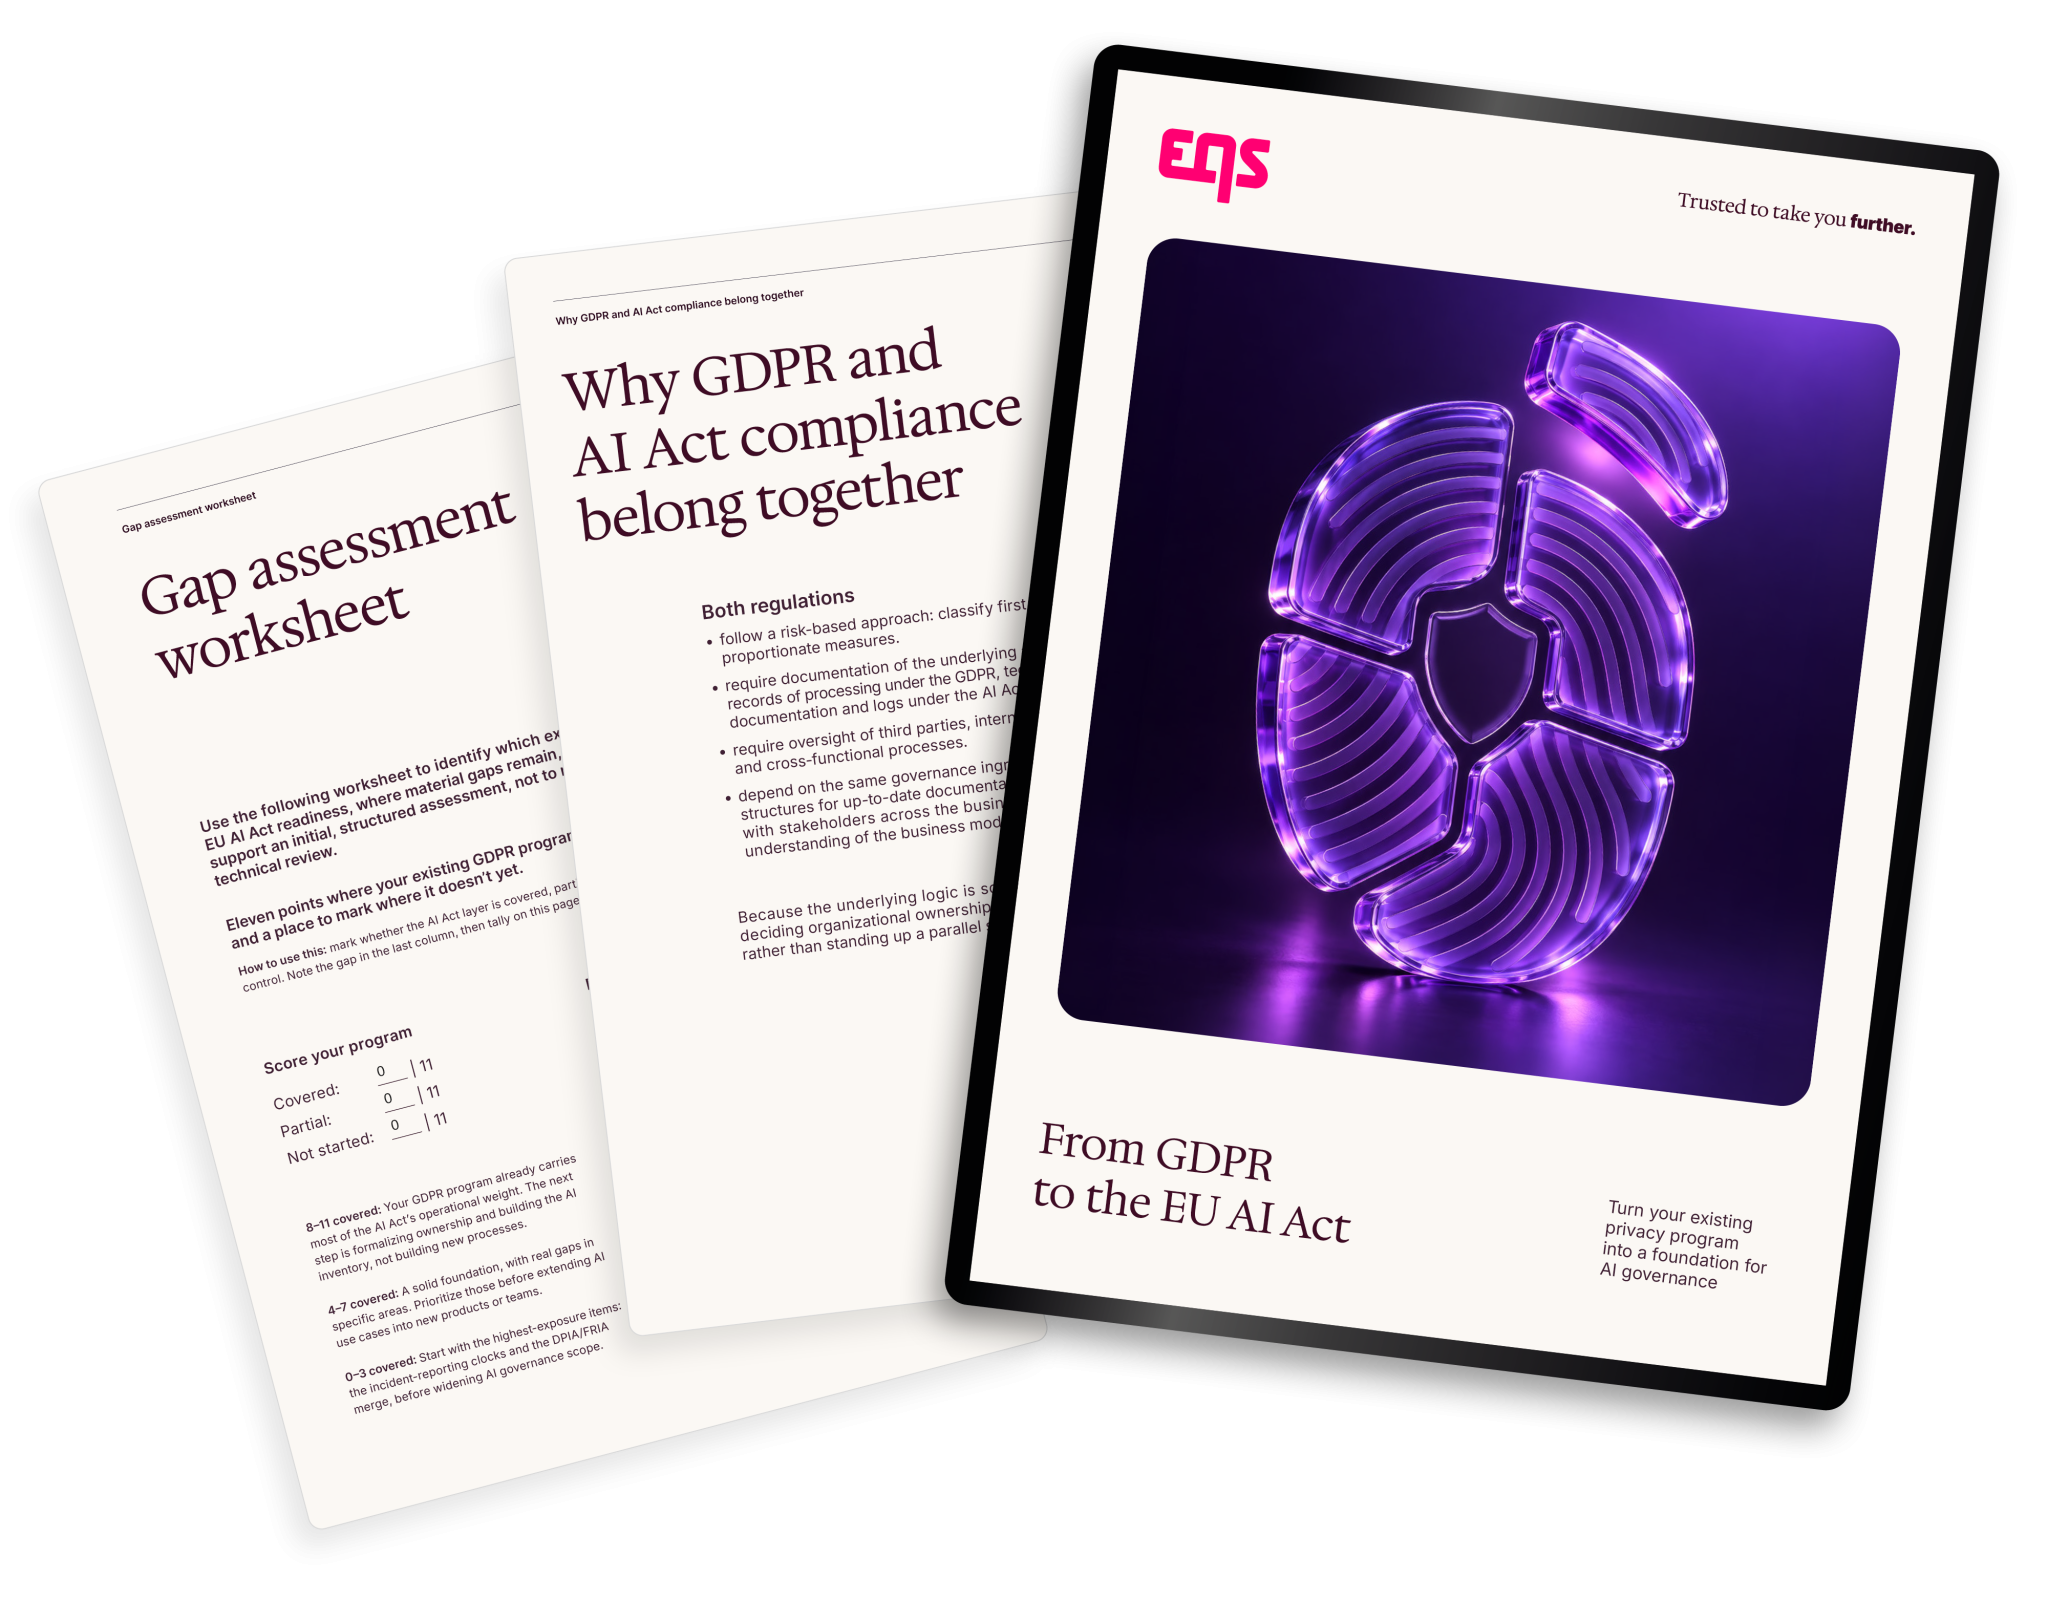
With article-level mappings and an 11-point gap assessment, this guide helps you distinguish reusable GDPR controls from AI-specific requirements and set informed priorities.

WHAT YOU’LL TAKE AWAY
A clearer basis for governance decisions: Explore how established GDPR structures can support AI-related risk management and accountability, while recognizing the boundaries between the frameworks.
A coordinated approach to impact assessments: Understand the distinct purposes of DPIAs and FRIAs, and where shared evidence can reduce duplicated effort when both apply.
A view of governance beyond deployment: Examine how incident reporting, alongside documentation and human oversight, connects privacy operations with ongoing AI responsibilities.
An actionable assessment of your position: Use the 11-point worksheet to evaluate existing coverage and identify gaps that require attention.
WHO IS IT FOR?
For DPOs and privacy leaders building their organization’s approach to AI governance, alongside compliance teams assessing how existing GDPR processes can support AI Act readiness.
WHY THIS GUIDE MATTERS
Fragmented governance creates costs that compound as AI adoption grows. Separate assessments consume resources, while disconnected reporting processes can leave responsibilities unclear.
A deliberate approach to GDPR and AI Act alignment helps leaders direct investment toward the capabilities their organization needs. This guide provides a concrete basis for those discussions, connecting legal obligations with operational decisions.
Download the Guide now
Sign up for our Compliance News Service and receive relevant updates. After successful registration, you will receive a download link by email. You can unsubscribe at any time.
Our Latest Resources
Explore our latest blogs, guides, and resources on compliance, data protection, and sustainability management.