


EQS Privacy Cockpit
Data Privacy Management Software for GDPR and EU AI Act
One platform to manage data privacy, meet GDPR requirements, and comply with the EU AI Act — powered by automation and AI.

Trusted by 14,000+ organizations globally for compliance and governance



GDPR and AI Act compliance challenges — and how to solve them
The regulatory landscape keeps expanding, while privacy and compliance teams aren’t growing at the same pace. The tools many teams inherit weren’t built for a world where GDPR, the EU AI Act, and risk obligations land on the same desk.
Privacy teams are no longer managing GDPR and other global privacy obligations in isolation. AI systems introduce new inventories, classifications, documentation, and risks. At the same time, organizations need a consistent way to identify, assess, mitigate, and report risk across business units and legal entities.
Managing each area through separate spreadsheets, tools, and local processes creates duplication and makes group-level oversight harder — a data privacy management software built to connect these areas removes that duplication by design.
One governance foundation for privacy, AI and risk
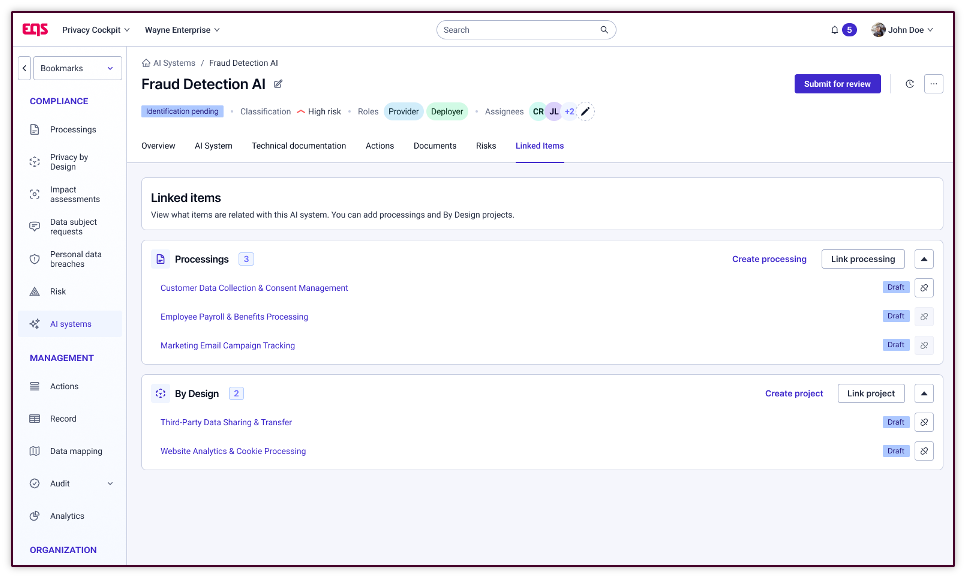
EQS Privacy Cockpit connects privacy compliance, AI governance and risk management structurally: AI systems link to the processing activities that use them, risks link to the evidence that mitigates them, and every workflow feeds a single audit trail.
That shared foundation gives privacy, legal, compliance and risk teams a common operating model: the same information, clear ownership, and standardized workflows, instead of different teams maintaining information in separate tools.
Each module below runs on the same foundation, so your platform grows with new regulatory obligations instead of adding a new silo for each one.
Modules at a glance
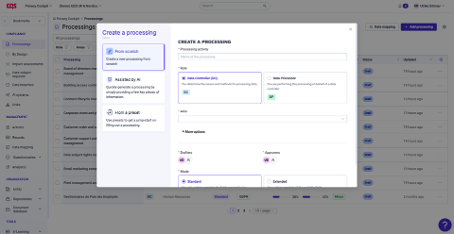
GDPR Compliance
Centralize your privacy program and manage the workflows DPOs rely on every day – from Records of Processing Activities and Privacy by Design to DPIAs, data subject requests, breaches, third parties and accountability documentation.
- Maintain centralized, multi-entity RoPAs with built-in automation and AI features
- Manage DPIAs and Privacy By Design workflows from a single template library
- Coordinate DSRs (DSR management) and data breach response on fixed timelines
- Connect stakeholders, tasks, documents, and evidence in one audit trail
- Monitor progress with dashboards built for DPO reporting
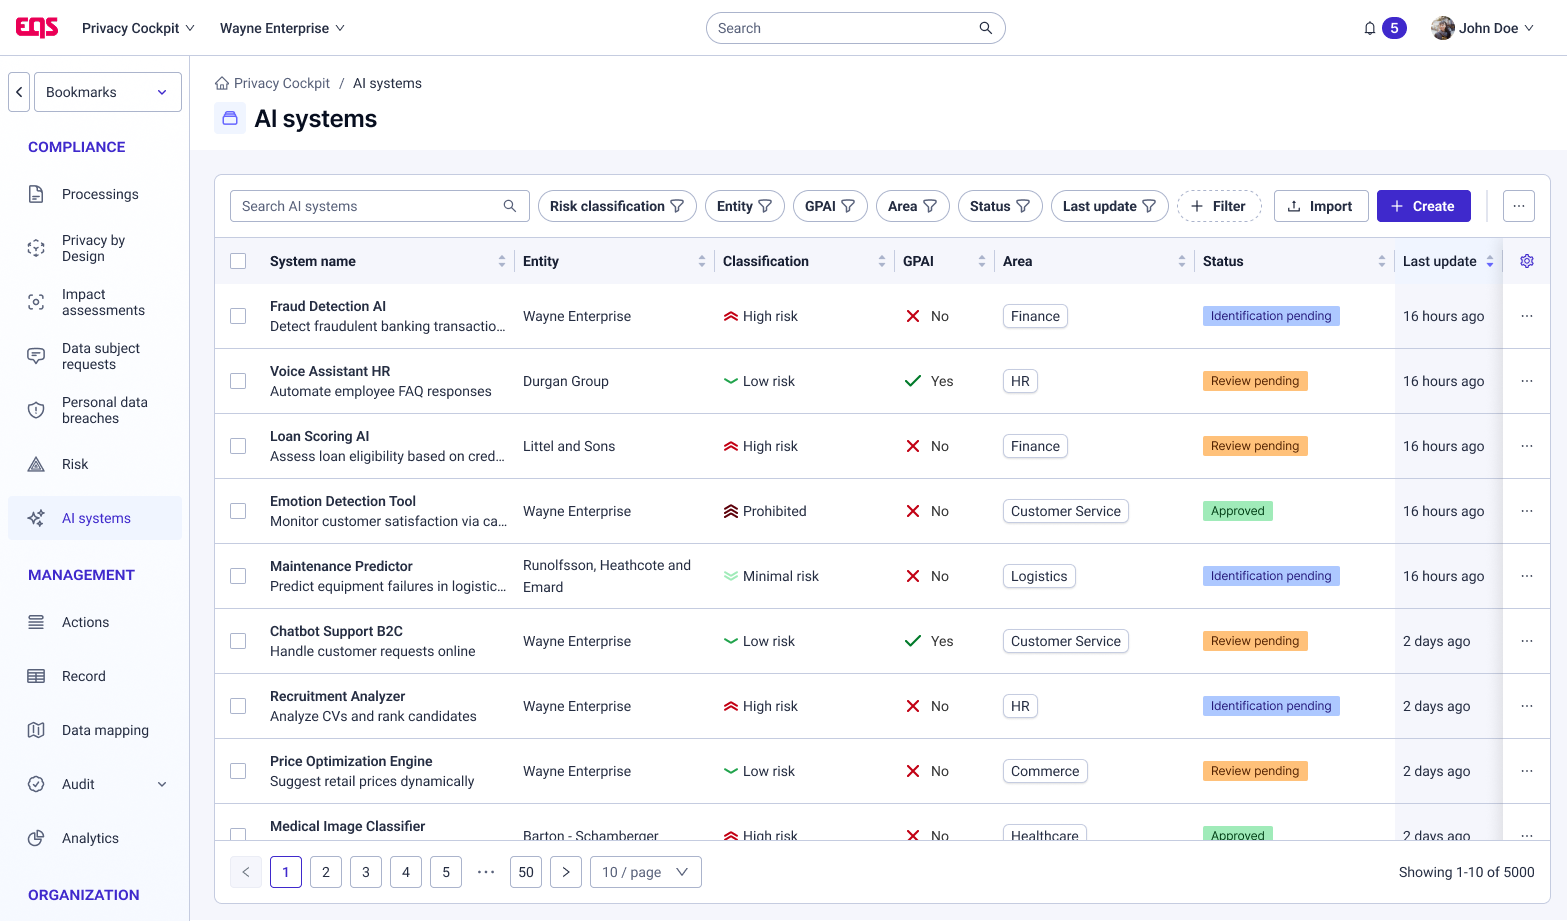
AI Governance
Create a central source of truth for the AI systems and models used across your organization. Structure ownership, classification, documentation, assessments, and governance decisions, while connecting AI activity to existing privacy and risk processes.
- Maintain a centralized AI system inventory across business units
- Document AI models, owners, providers, and use cases in one record
- Apply AI risk classification and map systems to relevant AI Act requirements
- Manage technical and governance documentation from a single workspace
- Guide systems through structured review and approval workflows
- Connect AI systems to processing activities, risks, and assessments — no duplicate documentation between GDPR and the AI Act
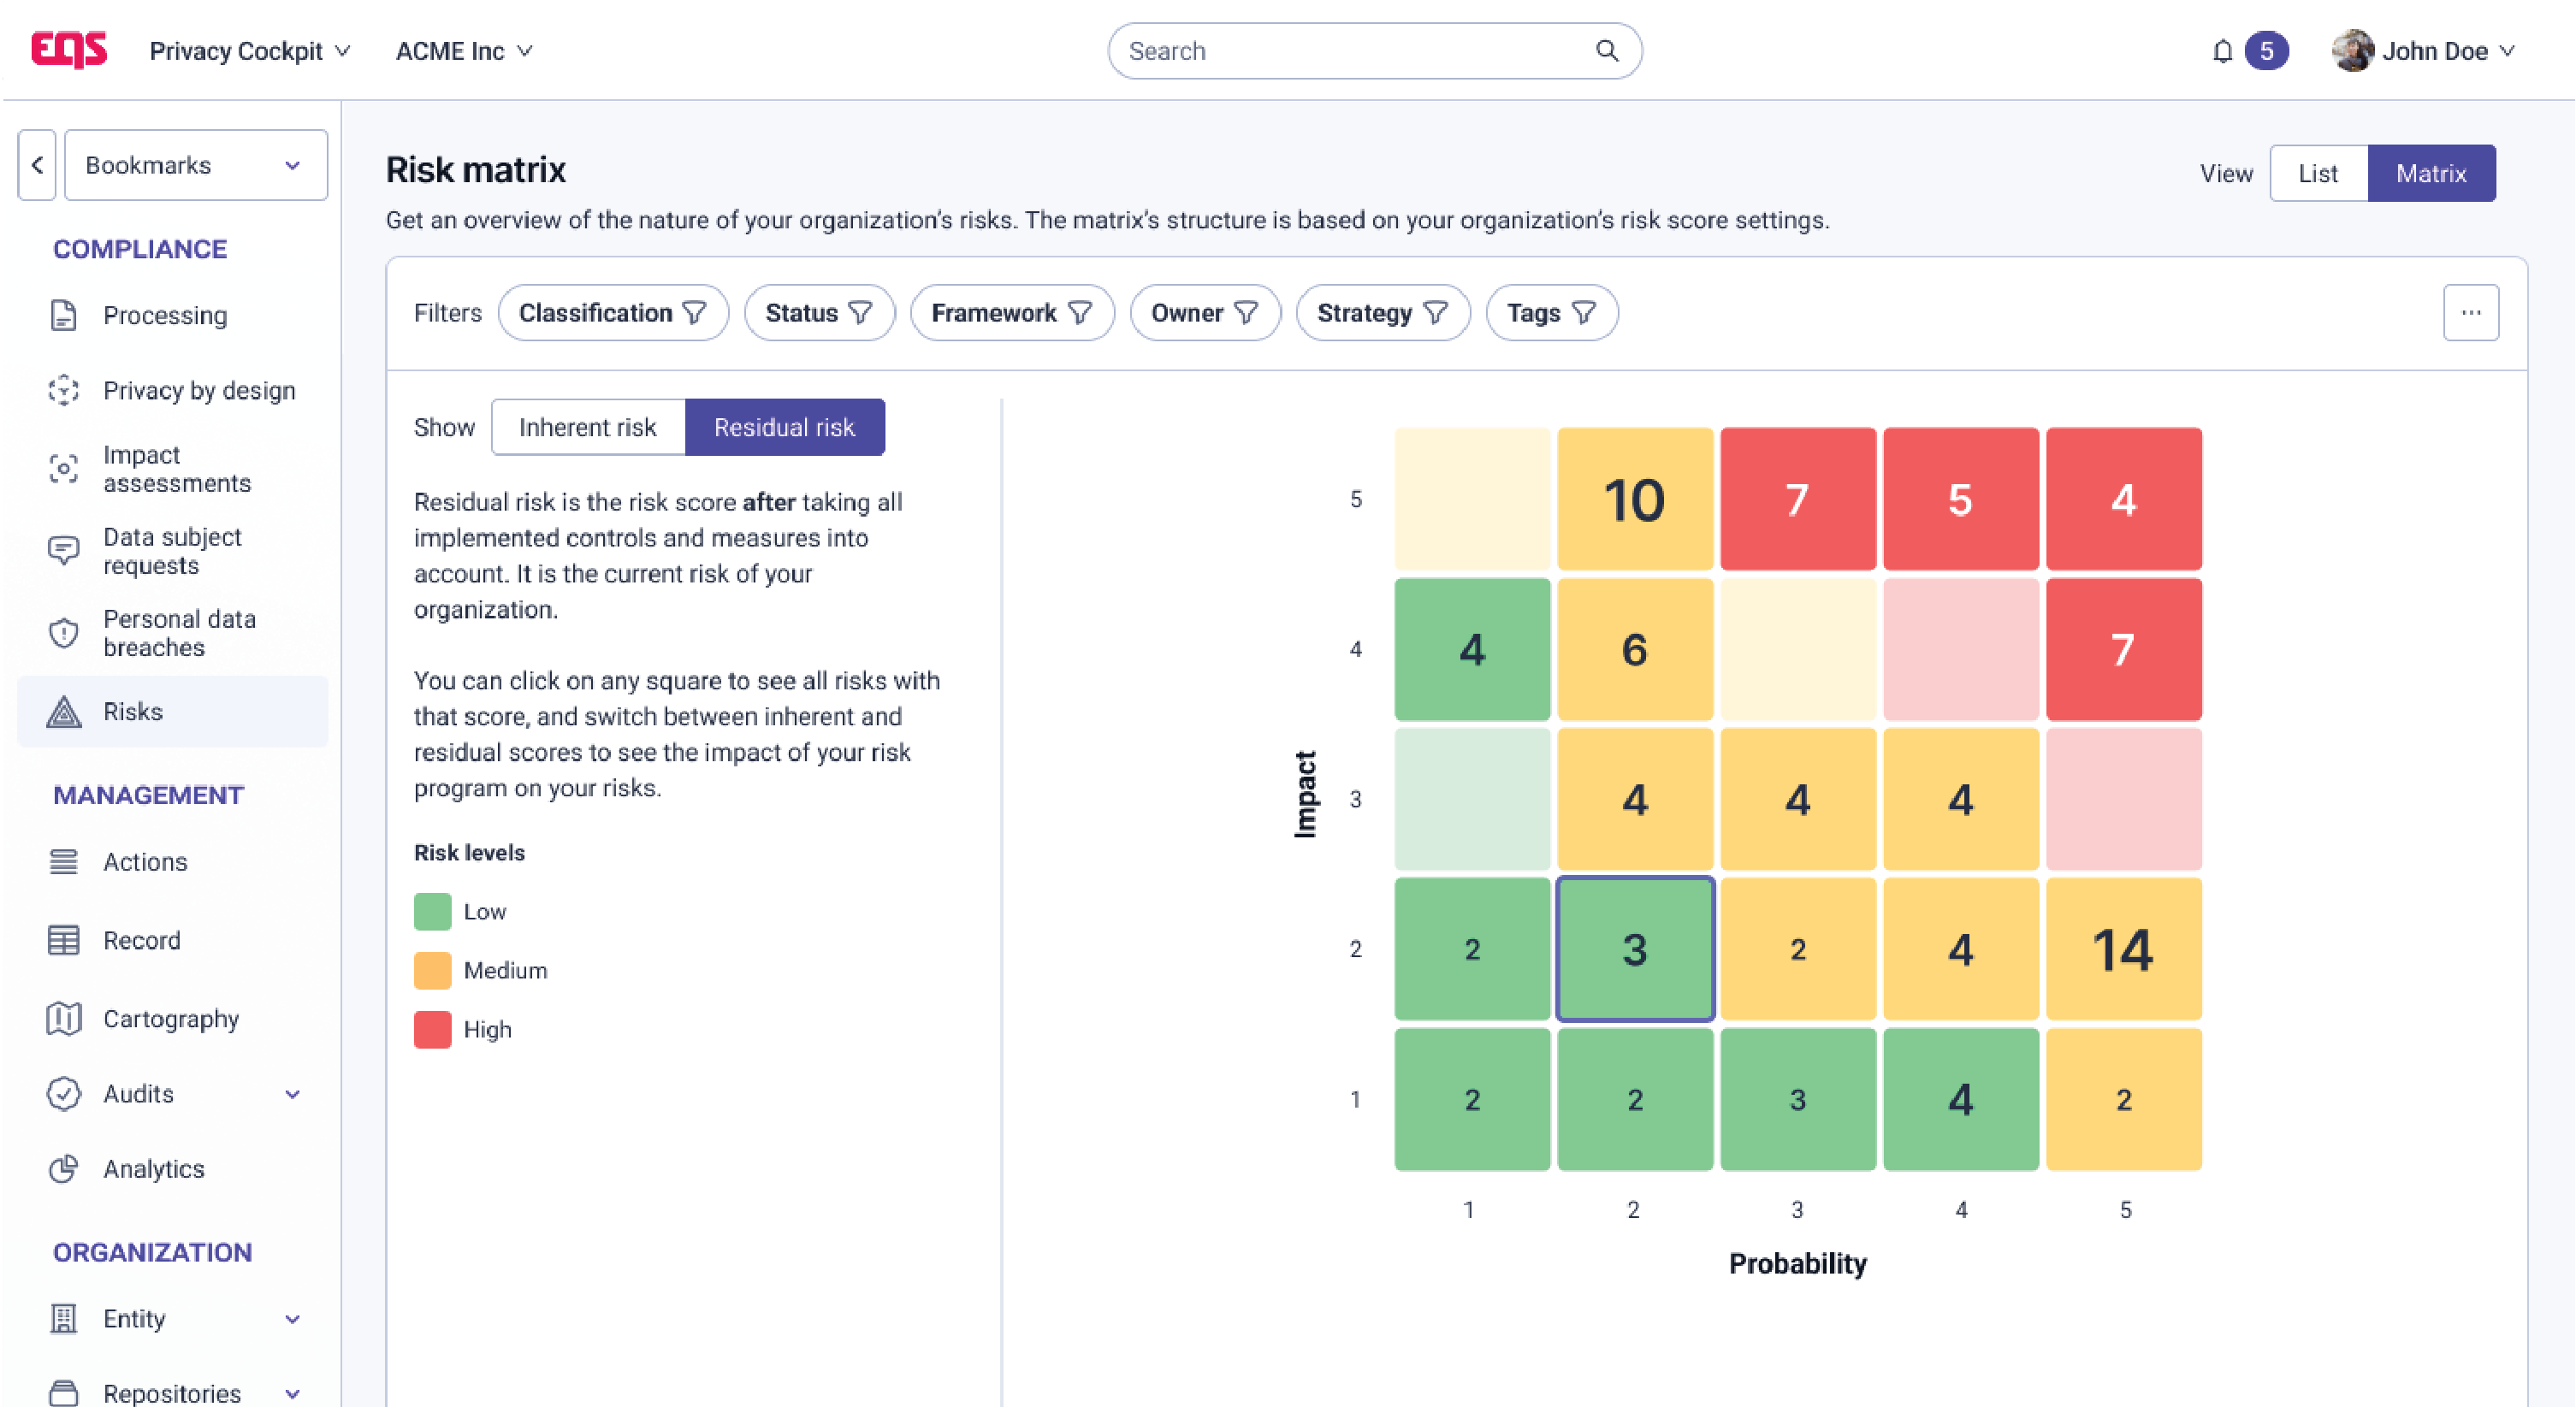
Risk Management
Identify and manage risk through a centralized risk register while connecting it directly to the privacy, AI, and compliance activities where it arises.
- Centralize risks, owners, and classifications in one register
- Assess impact, likelihood, and inherent vs. residual risk
- Link risks to controls, mitigation actions, and the data processor compliance records behind them
- Standardize risk methodology across entities
- Visualize exposure through risk matrices, dashboards, and KPIs
- Track remediation, responsibilities, and deadlines end to end
What our customers say
“The EQS Privacy Cockpit meets our requirements for a central yet decentralized compliance tool. Its user-friendly interface and multilingual support make it easy to roll out across all our business units.”

Danièle Lefur
Group DPO at Econocom
Highest security standards
The EQS Privacy Cockpit operates on ISO 27001 certified infrastructure, offering EU high-availability servers and guaranteed GDPR-compliant data management.
EQS Privacy Cockpit –
The governance platform seamlessly integrated in your processes.
The privacy, AI and risk management platform EQS Privacy Cockpit provides the infrastructure DPOs and compliance teams need to maintain continuous compliance without manual overhead.
One connected governance platform
Privacy, AI and risk information can be managed within the same governance environment instead of creating additional compliance silos.
Adapting to regulatory change
The EQS Privacy Cockpit platform supports organizations in operationalizing governance processes around global regulations and frameworks.
Built for multi-entity organizations
Standardize group-wide governance while maintaining the roles, permissions and flexibility needed locally.
Configurable workflows
Adapt workflows, responsibilities and assessments to your organization’s governance model.
Traceability by design
Maintain histories, documentation, responsibilities, actions and evidence as part of everyday processes.
Built for specialists and operational teams
Enable privacy, AI, risk and business stakeholders to contribute through structured, guided processes.
Frequently asked questions about GDPR and EU AI Act compliance
What is a data privacy management software?
A data privacy management software is a centralized platform that helps organizations run their privacy program — covering GDPR obligations, EU AI Act requirements, risk management, and employee training — from one system instead of scattered spreadsheets and point tools. DPOs and compliance teams use it to standardize processes, keep evidence audit-ready, and give leadership a single view across entities. EQS Privacy Cockpit is built specifically to connect these areas rather than manage them in isolation.
How does EQS help with EU AI Act compliance?
EQS Privacy Cockpit gives you a central inventory of the AI systems and models in use across your organization, with built-in classification against AI Act risk categories and structured documentation workflows. Because AI systems are linked to the processing activities and risks that already exist in your GDPR program, you avoid documenting the same system twice — the GDPR and AI Act workflows share the same underlying data.
What is a RoPA and how does EQS automate it?
A Record of Processing Activities (RoPA) is the inventory of data processing activities required under GDPR Article 30. EQS automates RoPA maintenance by connecting each record to its owner, legal basis, related risks, and third parties, and by prompting updates when an activity changes — rather than requiring a manual annual review of a static spreadsheet.
How long does implementation take?
Implementation timelines vary by scope, but most organizations move from kickoff to a working RoPA and initial workflows within a few weeks, with fuller rollout across modules and entities over the following months. EQS’s onboarding and customer success teams are involved throughout, not just at go-live.
Is EQS Privacy Cockpit GDPR-sovereign and made in Europe?
Yes. EQS Privacy Cockpit is hosted within the EU, ISO 27001-certified, and built with no data transfer outside the EU — a structural difference from platforms built on US-based infrastructure.
How does EQS handle the overlap between GDPR and the EU AI Act?
Rather than running separate assessments, EQS lets teams manage the Fundamental Rights Impact Assessment (FRIA) and Data Protection Impact Assessment (DPIA) in one unified workflow, so the same evidence and documentation serve both obligations instead of being duplicated across two processes. See GDPR Compliance and AI Governance for how each module works on its own.
Connect Privacy, AI and Risk in one governance platform
See how EQS Privacy Cockpit can help you centralize governance, standardize workflows and build clearer oversight across privacy, AI and risk.
Dikran Tabbakh
Account Executive
Book a demo